
Welcome to windows-noob.com!
Logging in will allow you to download scripts used in the guides.
If you came here looking for the Endpoint Manager step-by-step guides then please start here.
Register for free and ask your questions in our forums.
- 3 replies
- 6873 views
- Add Reply
- 5 replies
- 7791 views
- Add Reply
- 2 replies
- 2357 views
- Add Reply
- 2 replies
- 2334 views
- Add Reply
- 3 replies
- 6999 views
- Add Reply
- 2 replies
- 2447 views
- Add Reply
- 4 replies
- 5853 views
- Add Reply
- 1 reply
- 3396 views
- Add Reply
Installing SCCM CB - Failed to find or create machine self-signed certificate on SQL Server

By hdddisco1,
Hi All,
First at all, Its a pleasure to sign in to this Forum. Thanks for your support!
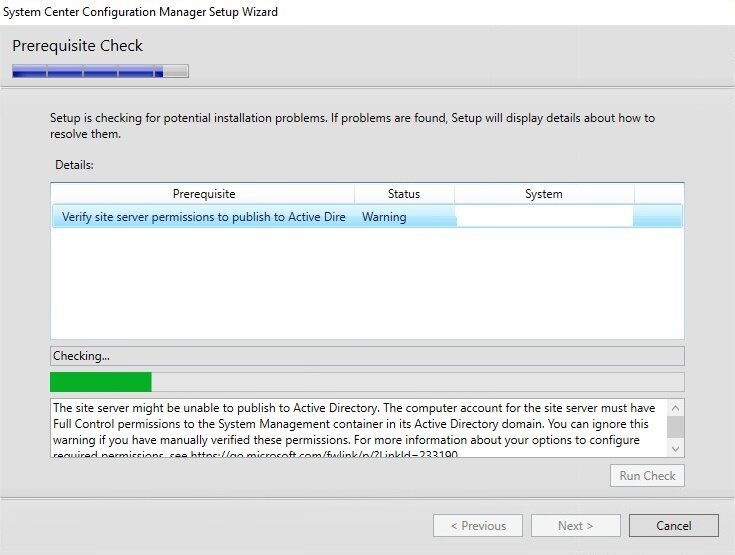
I'm working on a secured environment and trying to install SCCM CB 1902 for a demo purpose and are stucking on an error during SCCM install on step "Generating self signed certificate on SQL Server..."
My insfrastructure:
- AD DC Windows Server 2016 with System Management container created and respective permissions asigned
- Remote SQL Server 2016 on Windows Server 2016.
SQL se
accidentally deleted task sequence

By CertisEU,
Dear,
I just discovered that my most important Task Sequence has been deleted by someone ...
Is there a way to restore this??
must appreciated if you can help me out!
best regards
Imaging to RAID volume

By COB TSS,
We have a machine with RAID card installed and configured that fails to image via PXE. When the task sequence gets to the partition disk step it immediately fails as it can't see any physical disks.
When installing from bootable USB, Windows was able to detect both the onboard RAID controller volume and the volume from the attached to the external RAID card.
Is there a way to make the task sequence see the RAID volume and complete Windows deployment.
Thank you
SCCM source location

By rob343,
Hi does any know of any tools to assist in moving the sccm source repository. For updating all the location on all packages, apps, drivers etc?
Thanks
Rob
Software Update Fails After Requiring SSL 8531
By MagnumVP,
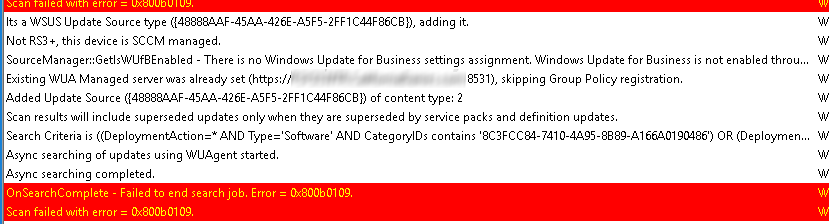
Client logs show: 0x800b0109
I have done all the standard checking for this error and nothing seems to resolve it. I'm allowing Third Party certs via GPO to all clients but they just won't scan. I exported the cert from the server and imported it on the client (which actually shows two in both locations because SCCM client put there there for me). All the logs indicate that it occurred last Wed the 22nd. This corresponds to the time I enabled 3rd Party Software Updates which generates a ne
Lost All Ability to Sync Updates - Since October 2019
By MagnumVP,

According to my SCCM I have not sync any updates from MS since October 2019. I have nothing for November through now.
The wsyncmgr.log shows it connects and syncs.
Unable to connect to WSUS Server
By MagnumVP,

The SMS_ISVUPDATES_SYNCAGENT.log is showing "Unable to Connect to local WSUS Server" every minute ans has been for days (the log only goes back 3 days and it's full with these messages).
I recently performed an in-place upgrade from 2012 R2 to what is now 1910 with Hotfix. So far everything seems to be working as expected but notices this last night and I'm not sure where to look.
I can connect to the local SQL DB where WSUS DB is located and connect to the SCCM DB as well.
PKI Certificate setup for Multiple Domain

By senthil,
Hi,
I have followed the below link on SCCM for HTTPS PKI certificate in my environment. But we have multiple domains.
Created the cert in 1 domain and able to see the Auto Enrollment Client Authentication certificate in windows 10 machine(same domain), but in other domain it is not working. All the Domains are trust releated but still not working
Would help me on PKI Certificate implementation in multiple domains
https://www.windows-noob.com/forums/topic/16300-how-can