
anyweb
-
Posts
9292 -
Joined
-
Last visited
-
Days Won
371
Everything posted by anyweb
-
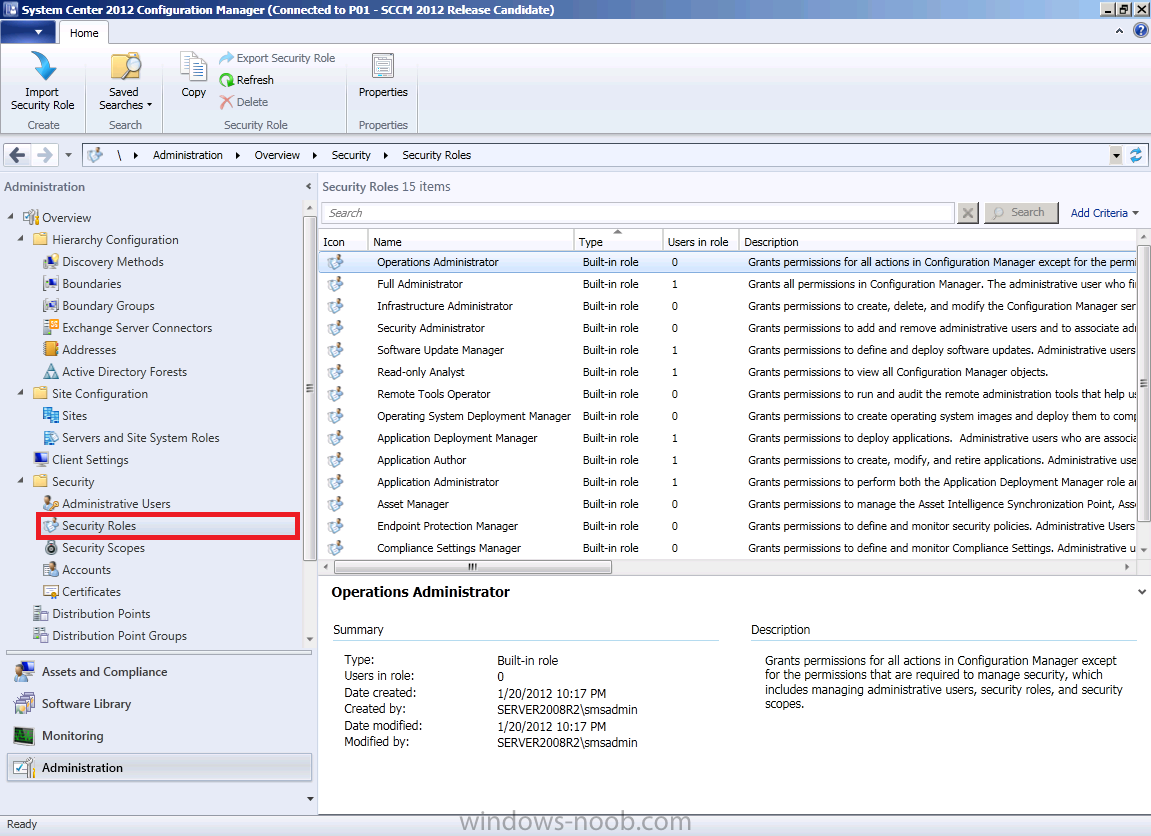
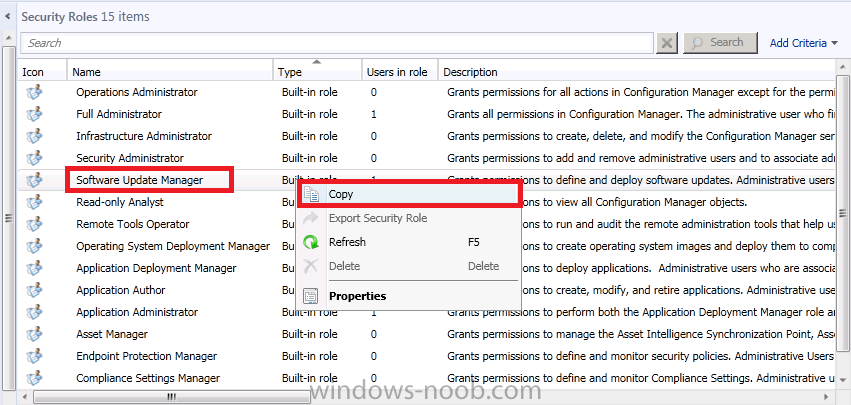
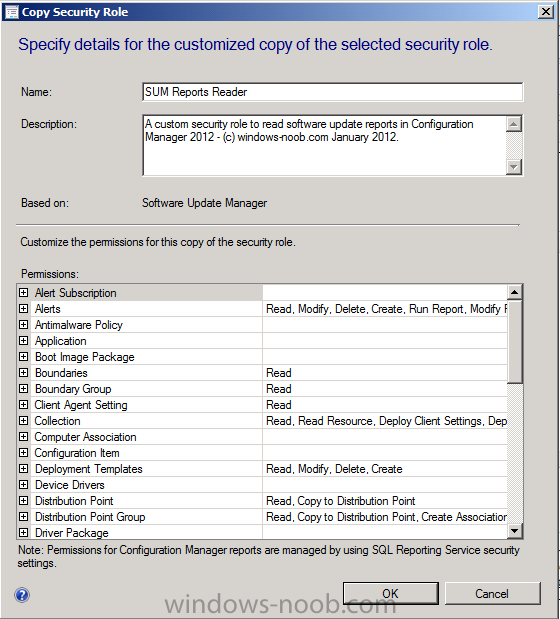
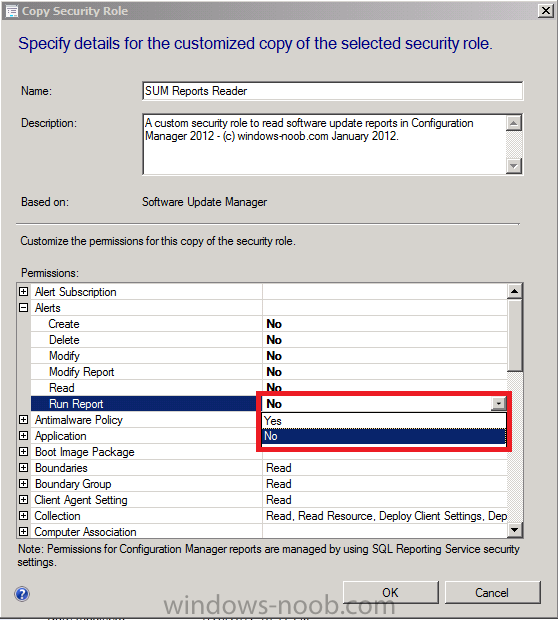
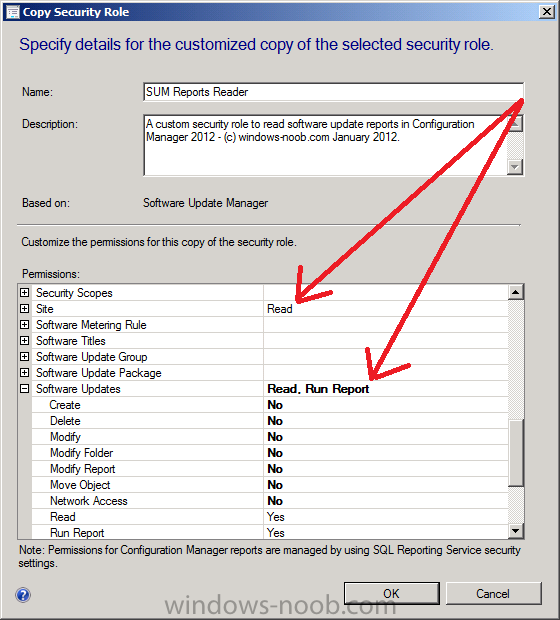
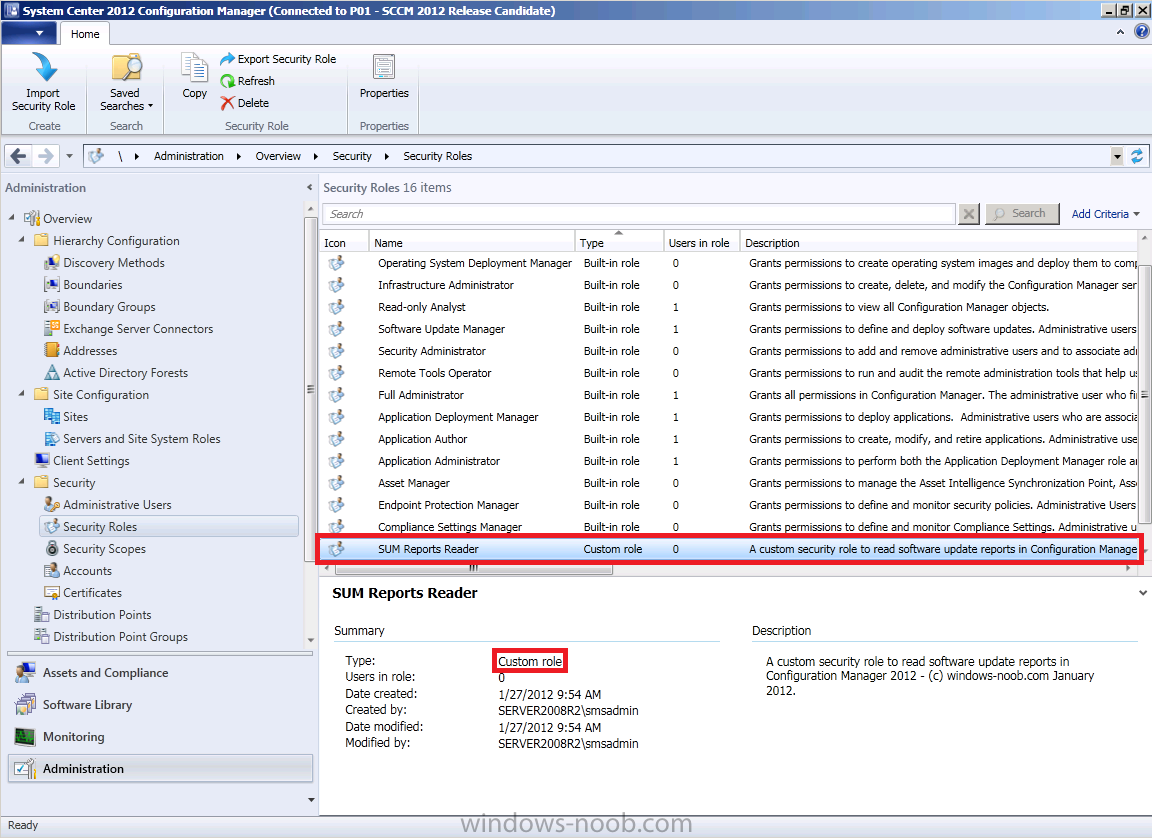
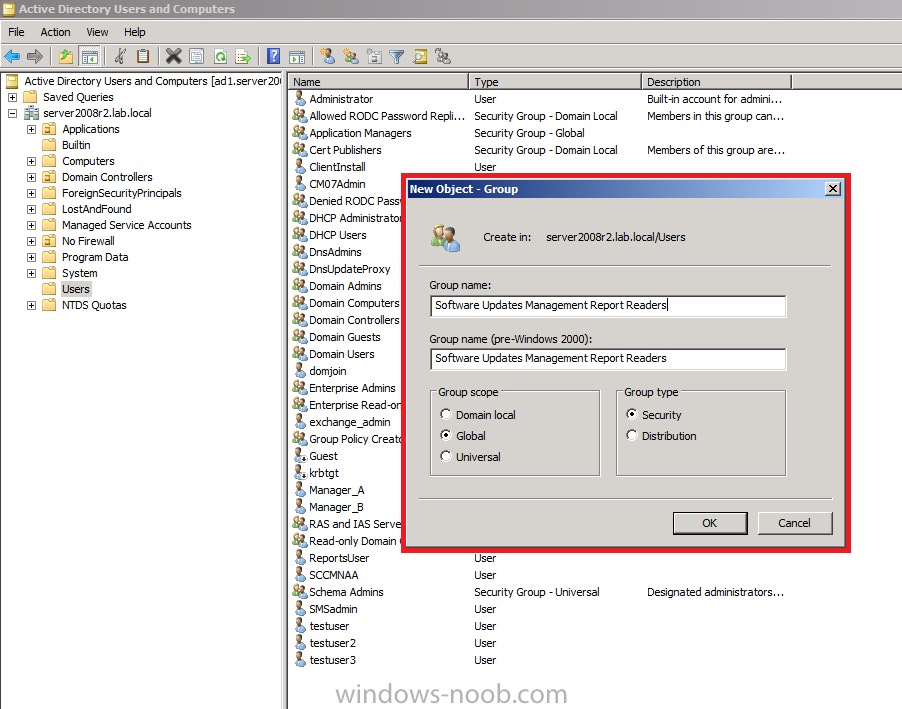
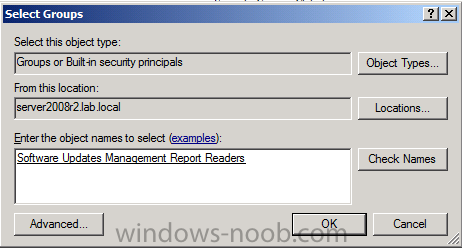
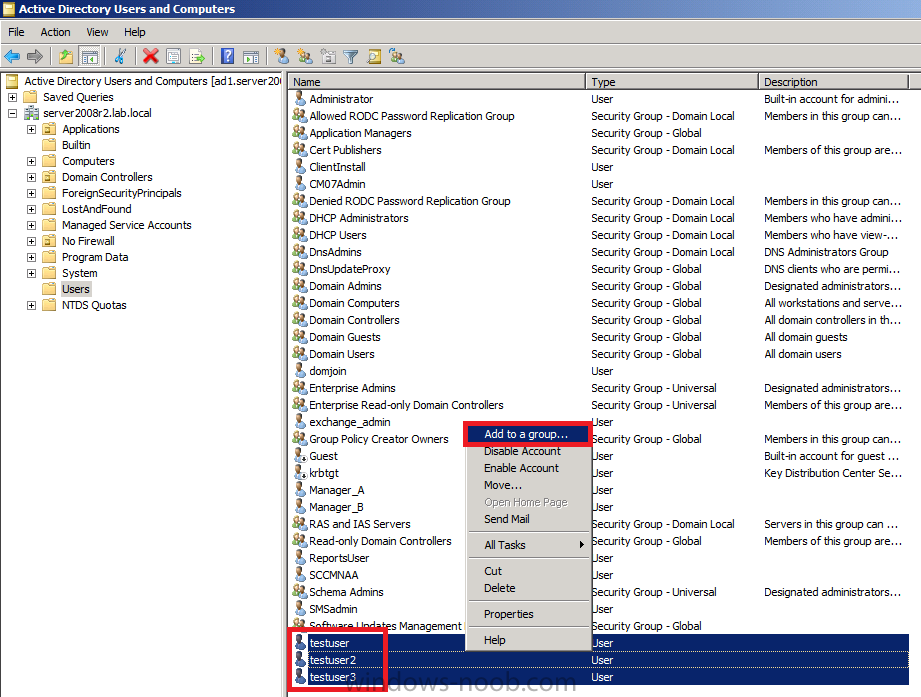
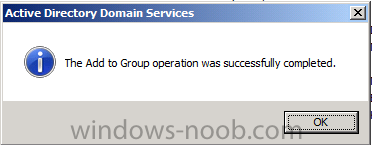
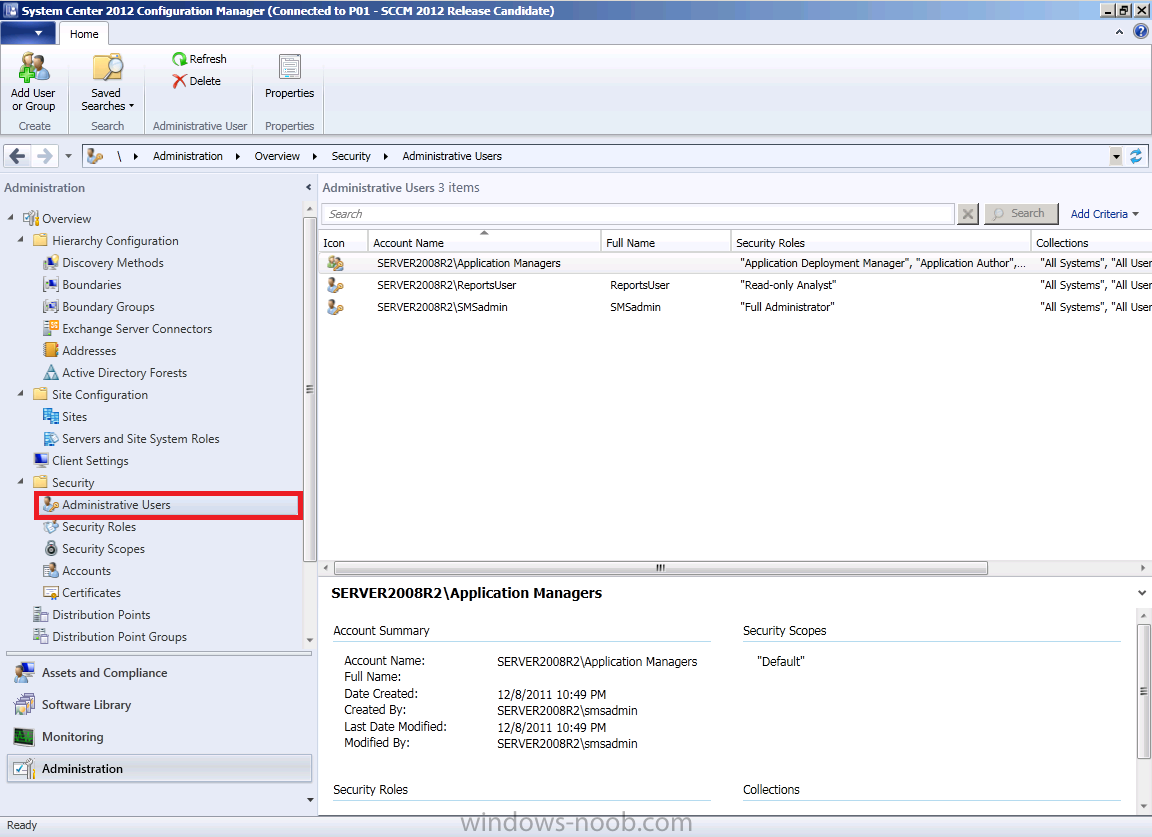
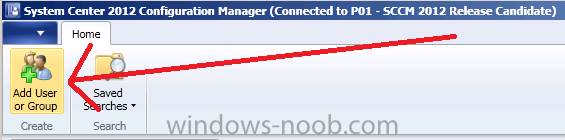
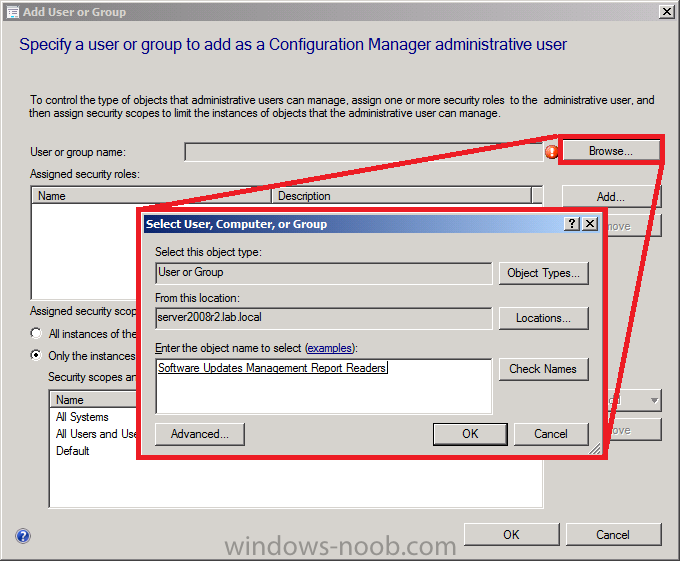
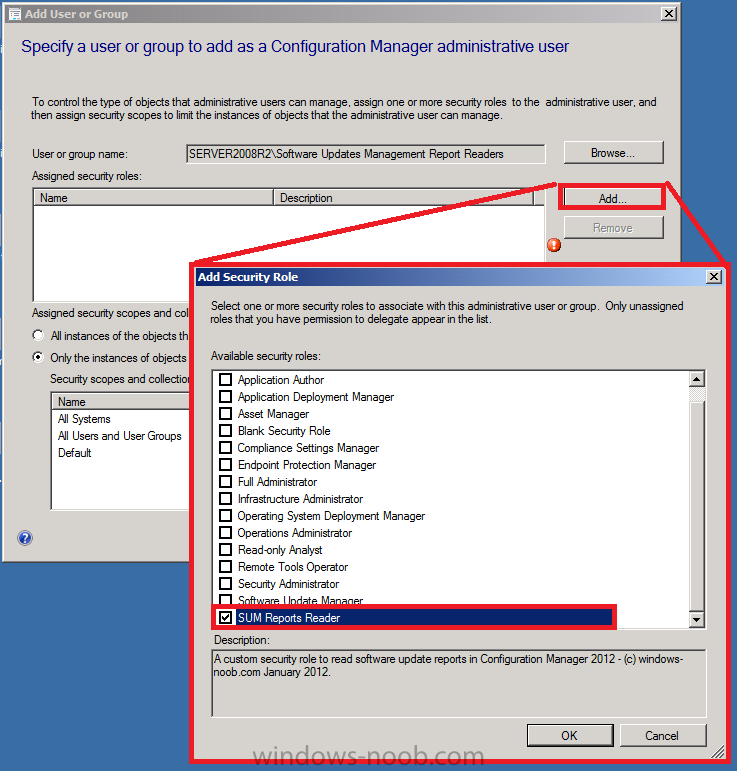
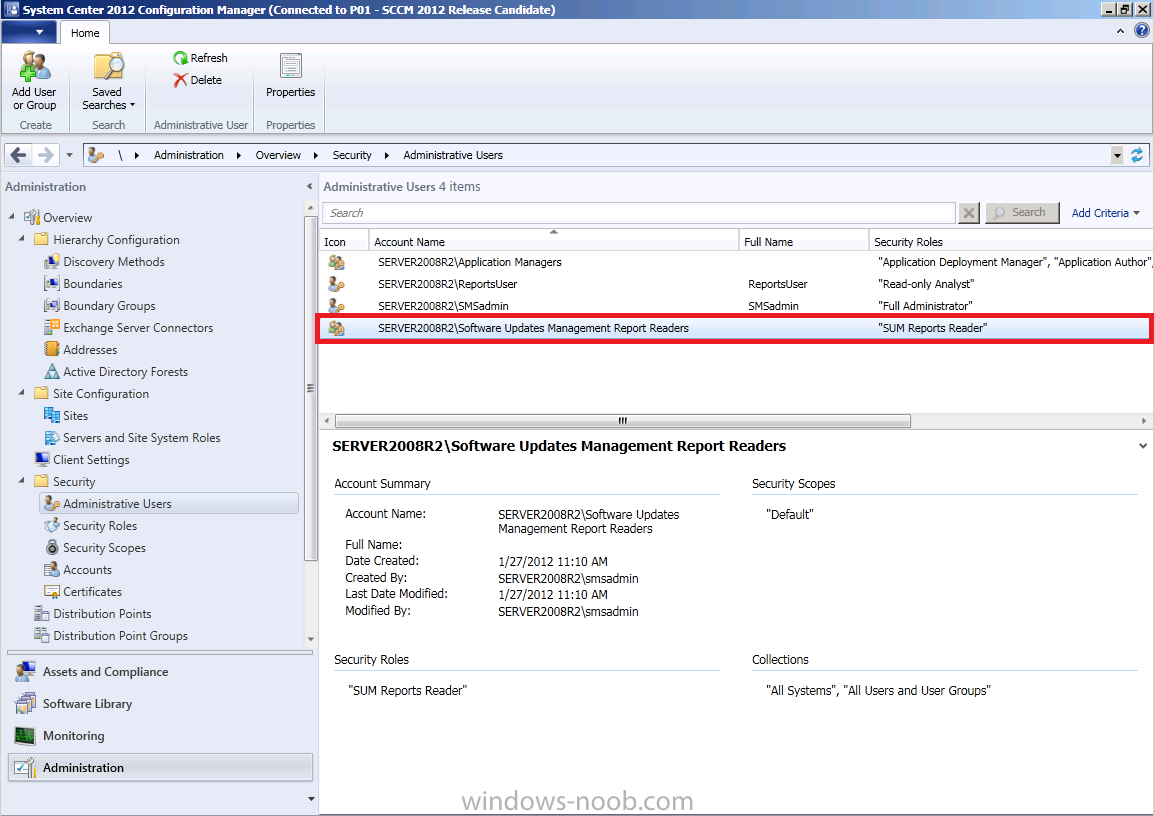
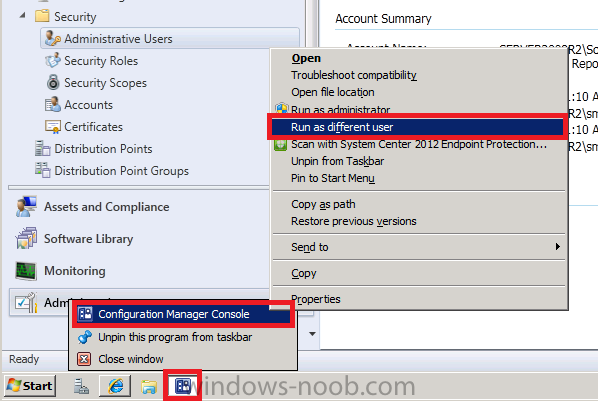
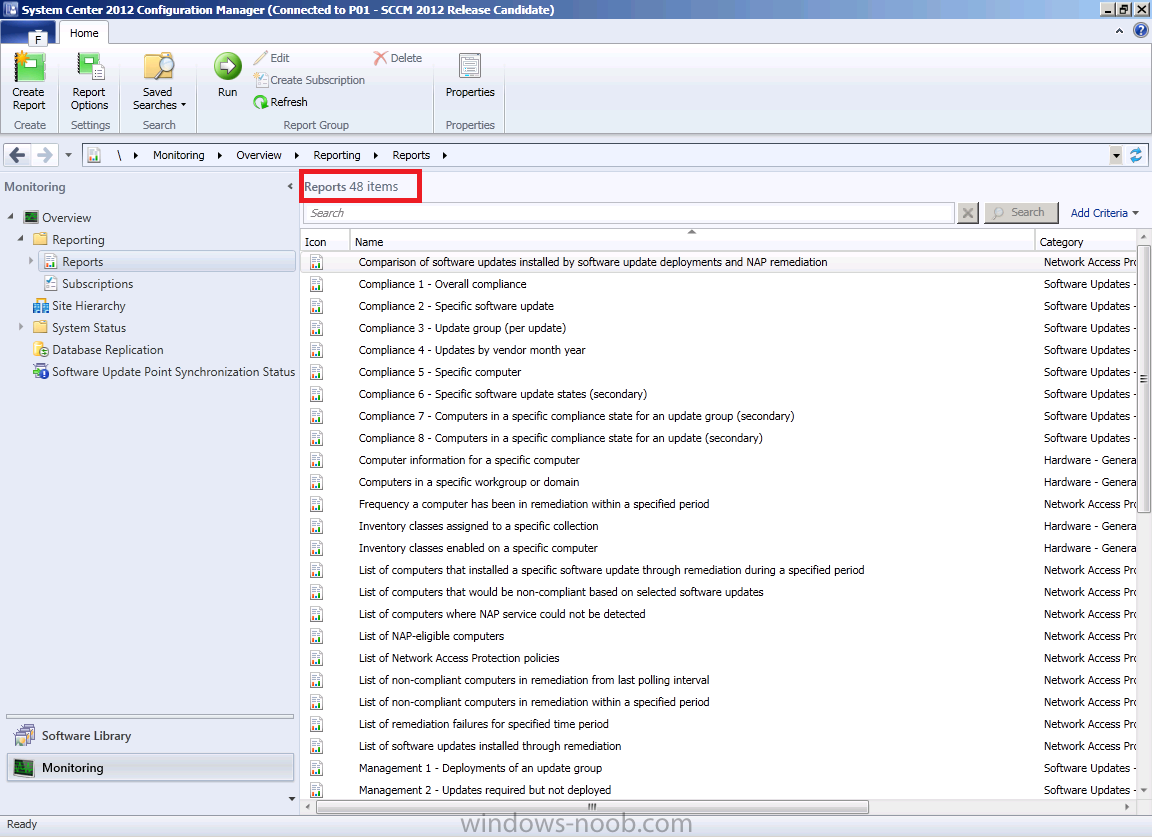
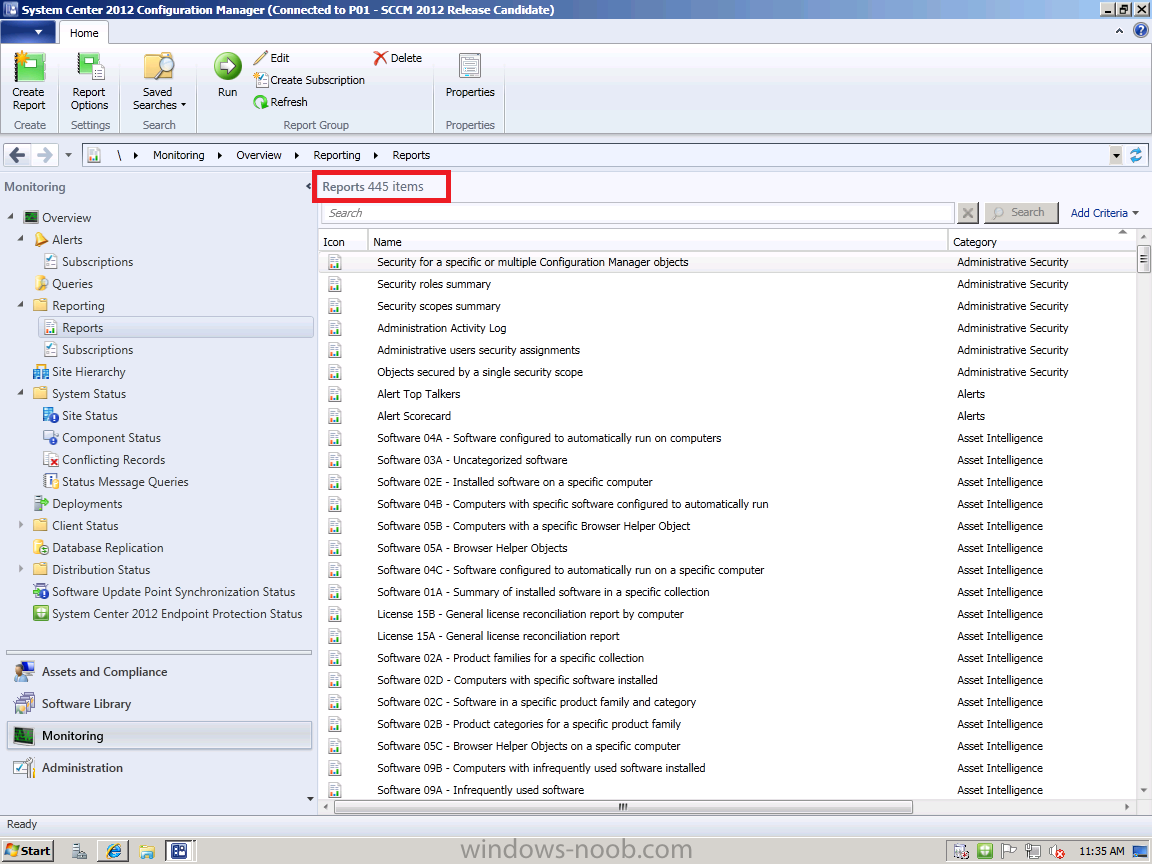
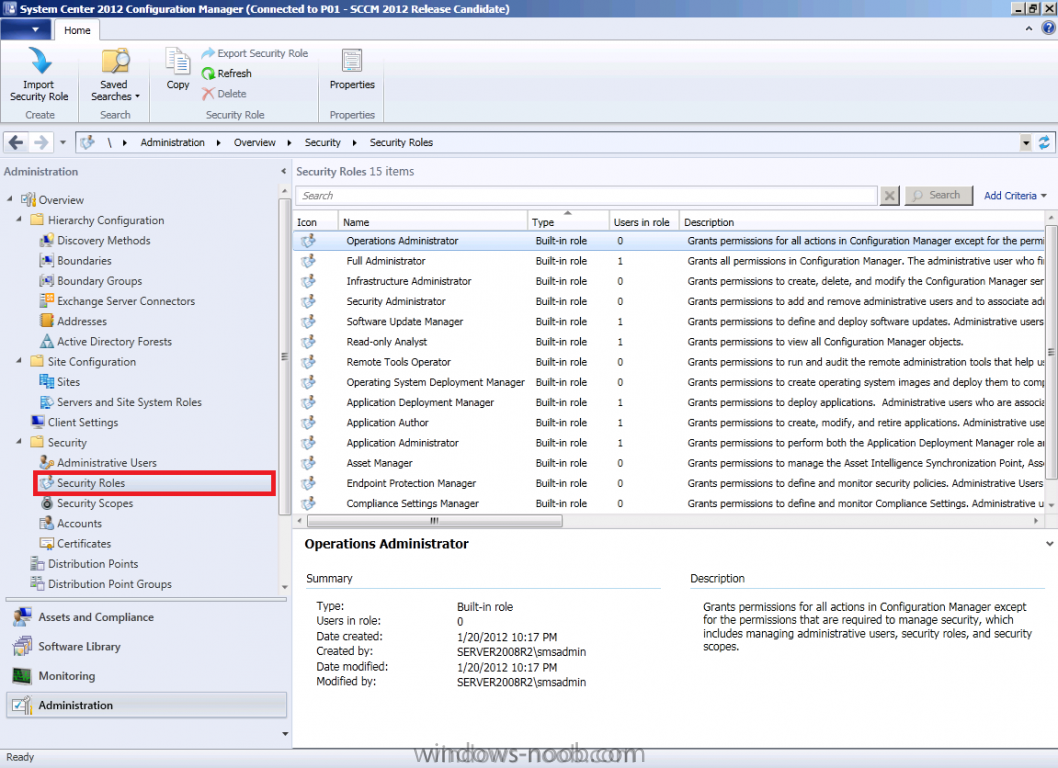
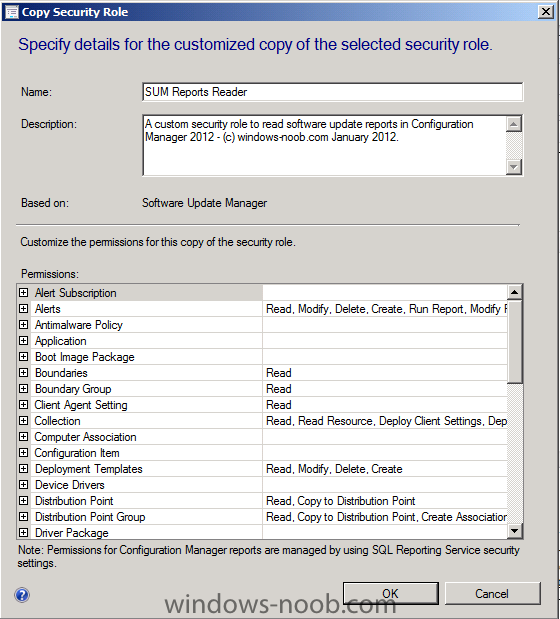
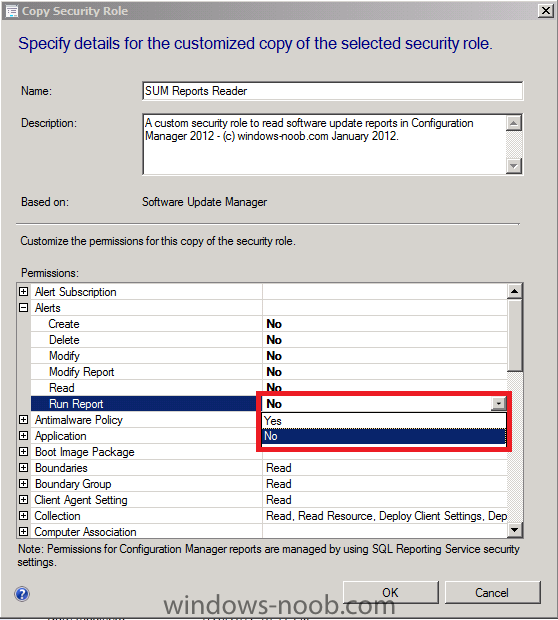
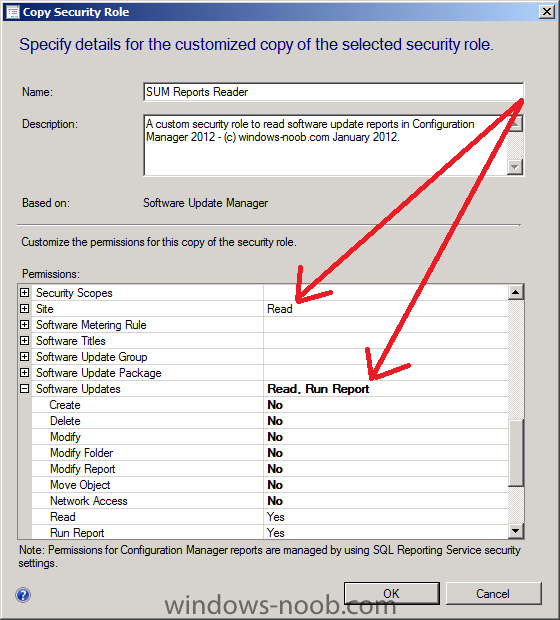
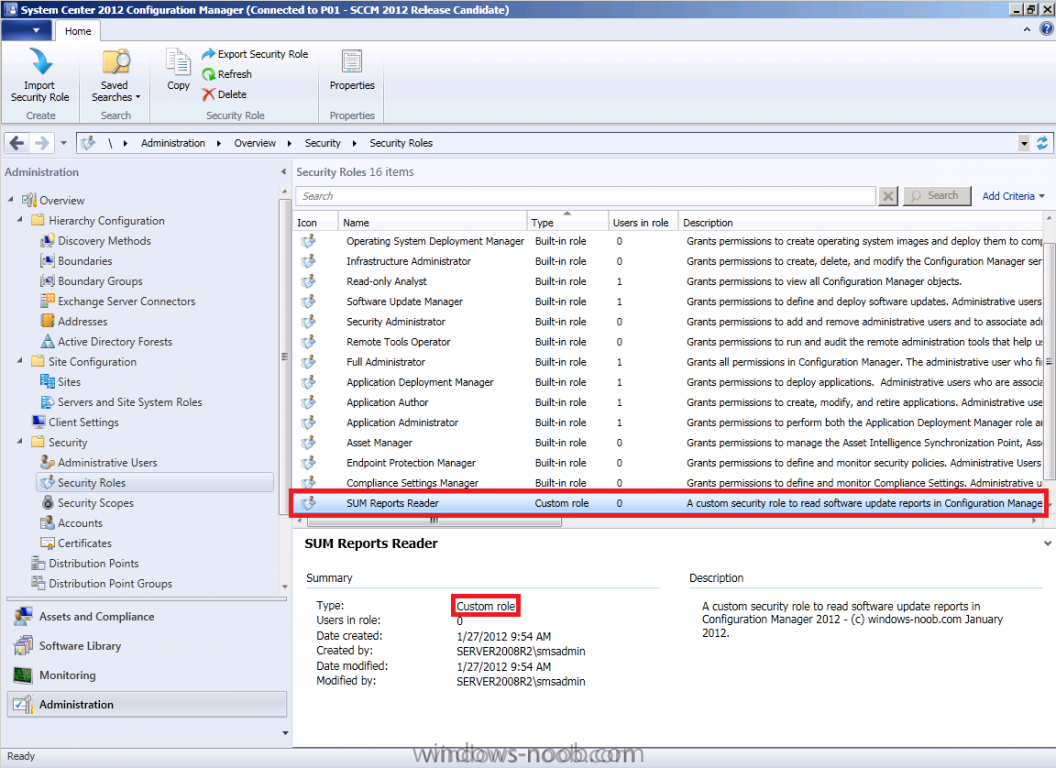
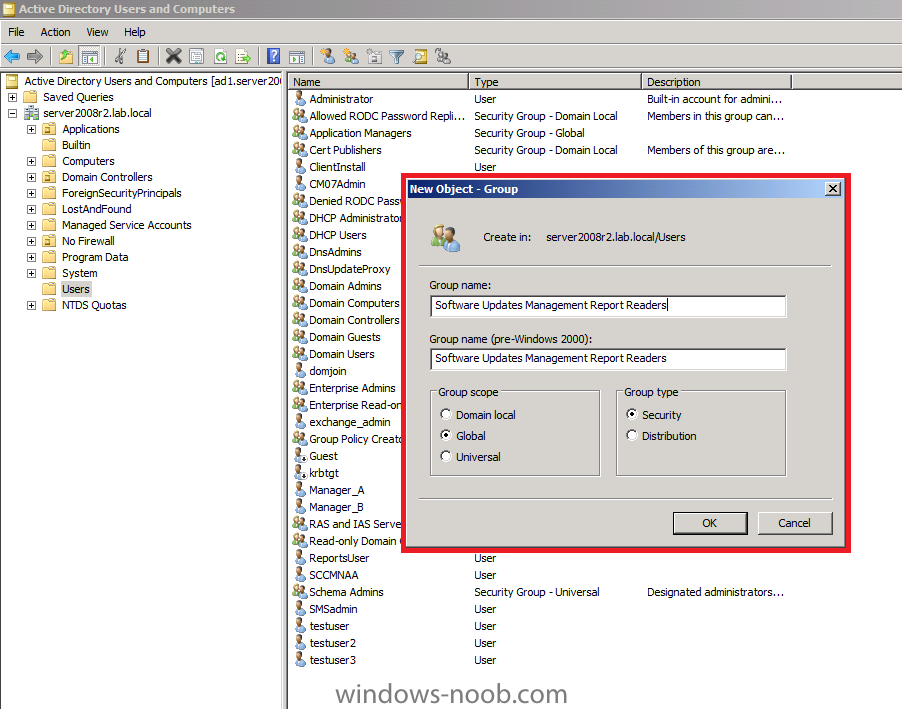
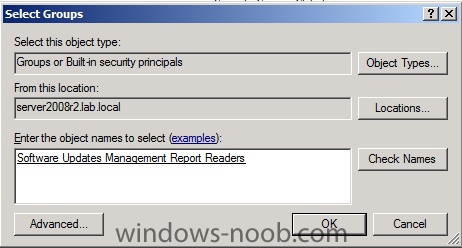
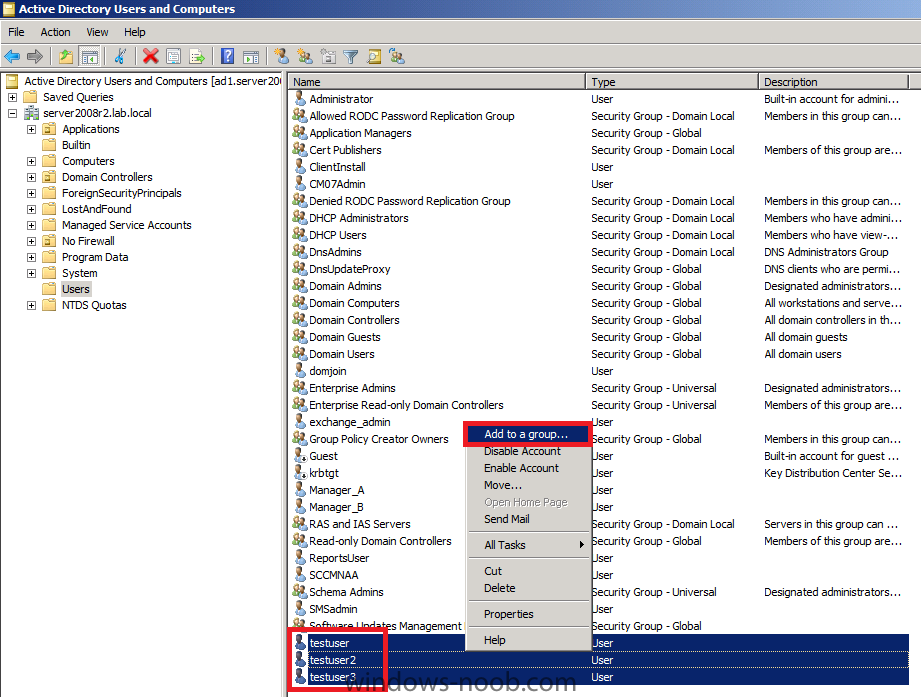
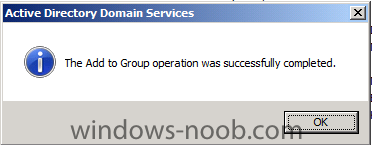
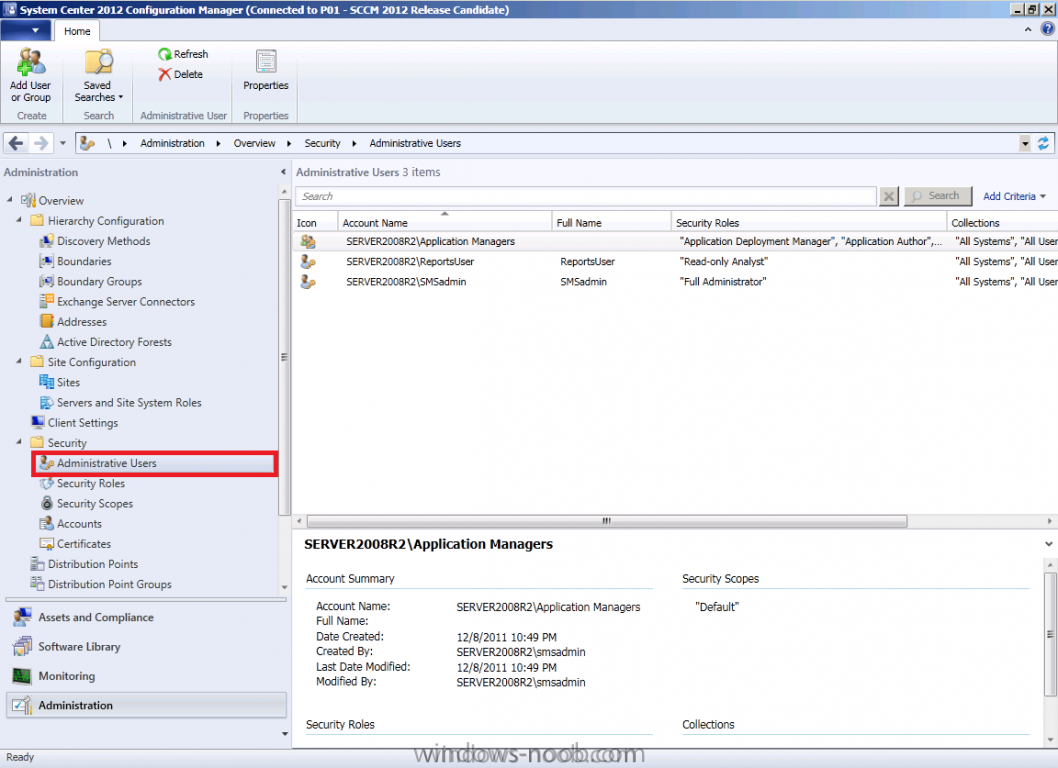
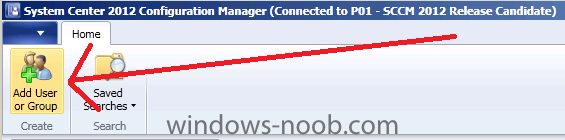
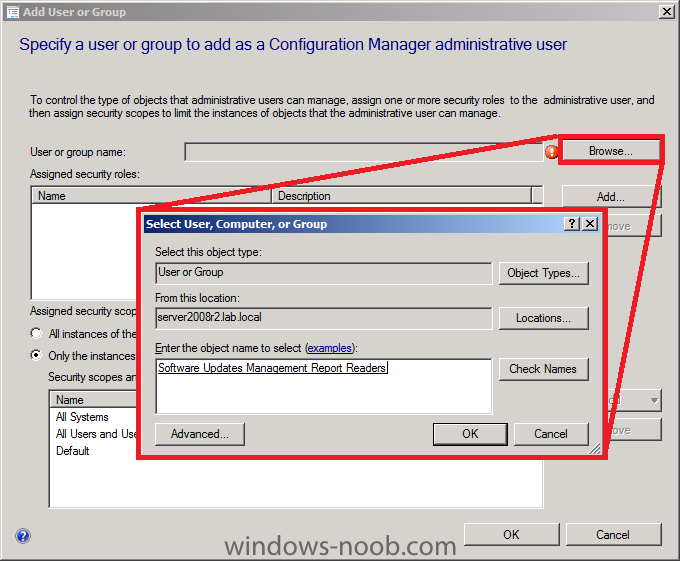
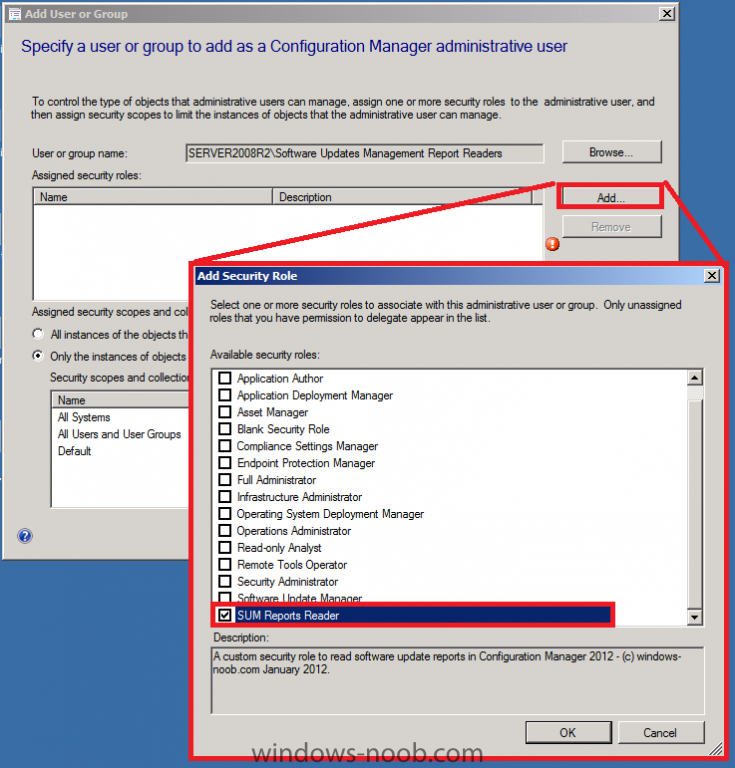
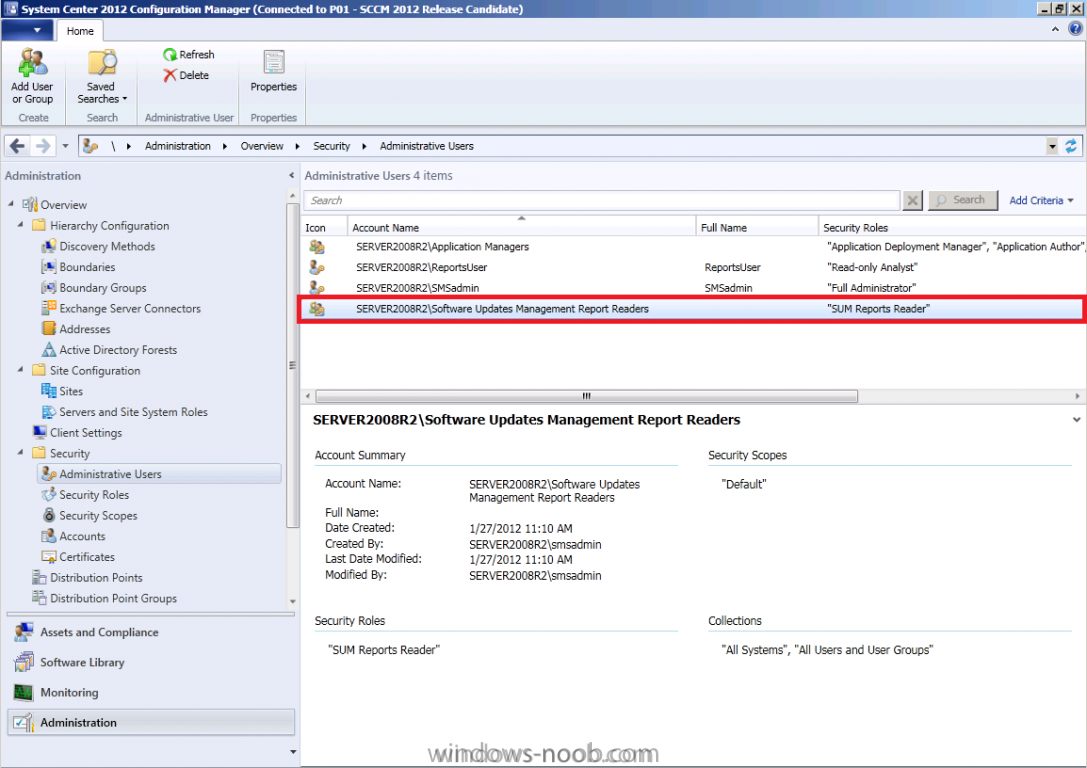
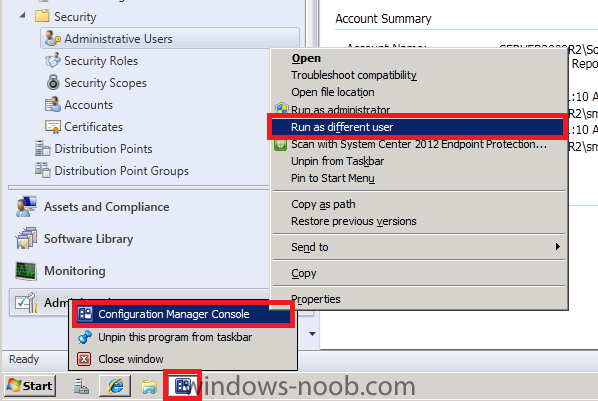
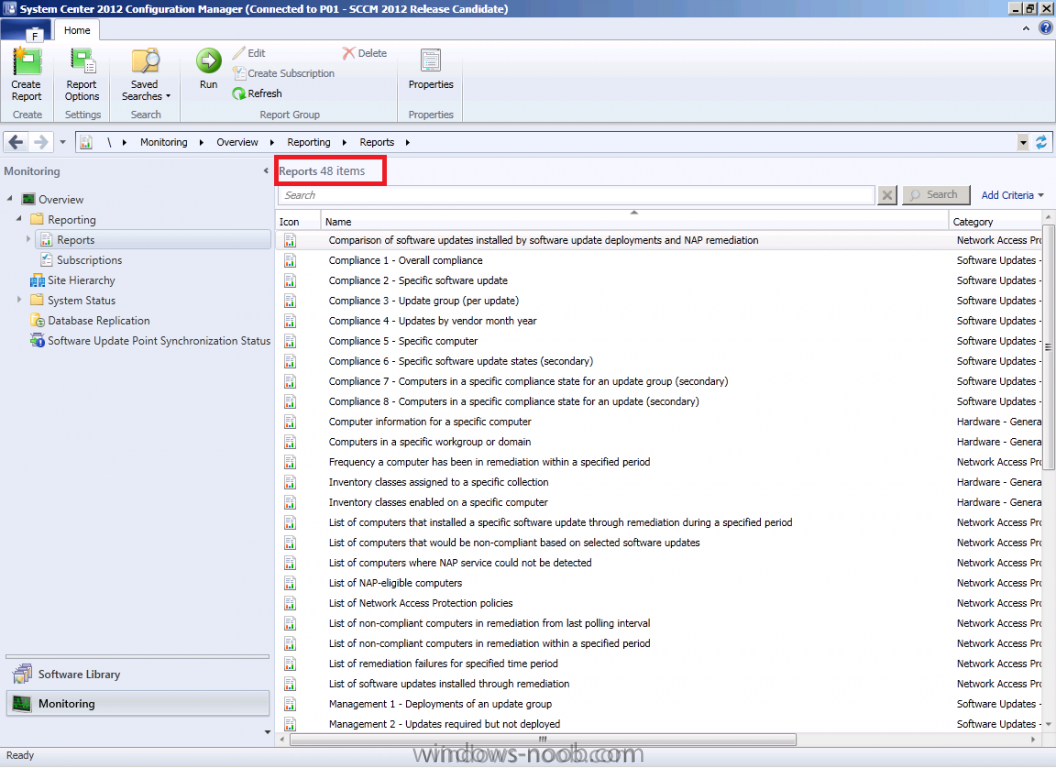
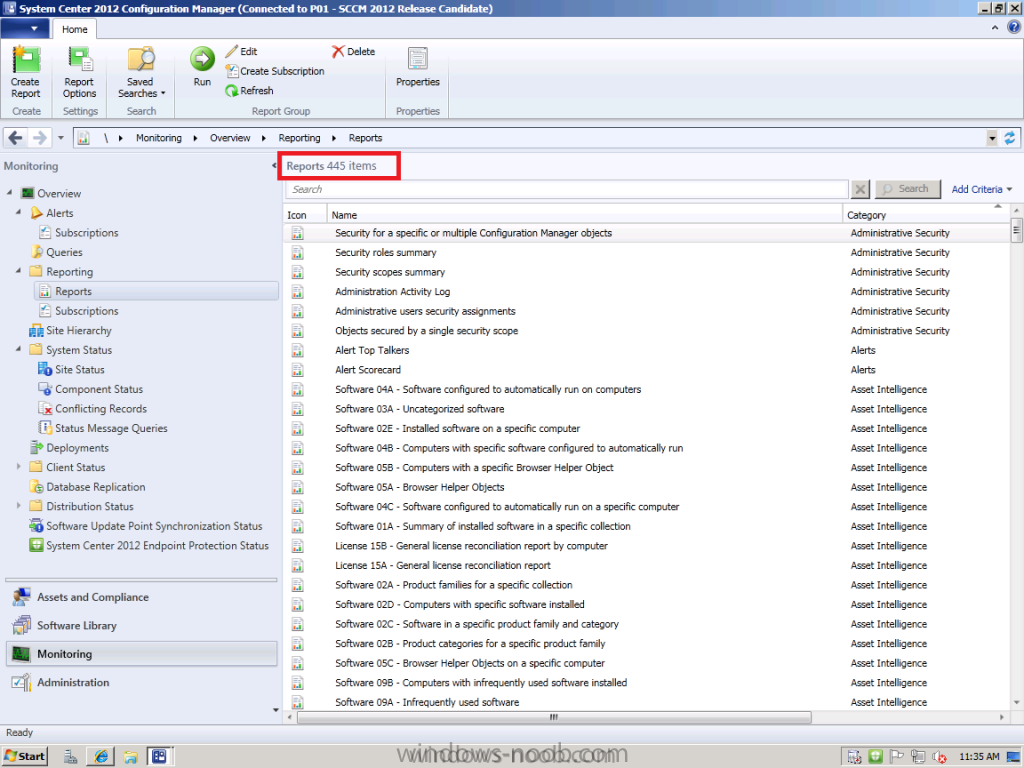
 In Part 1 of this series we got our AD and SCCM servers ready, and then we installed System Center 2012 Configuration Manager as a standalone Primary site. In Part 2 we configured the SCCM server further by adding some Windows Server roles necessary for the following Configuration Manager 2012 functionality, Software Update Point (SUP) and Operating System Deployment. In Part 3 we configured the server further by Enabling Discovery methods and creating Boundary's and Boundary Groups. In Part 4 we configured Client Settings, Added roles and Distributed the Configmgr Client to our Computers within the LAB, then in Part 5 we enabled the Endpoint Protection Role and configured Endpoint Protection settings and targeted a collection called All Windows 7 Computers with these settings and policies. In Part 6 we configured our SUP further to Deploy software updates to our All Windows 7 Computers and Build Windows 7 X64 collections. In Part 7 we used the Build and Capture process to create our Base Windows 7 X64 wim image. In Part 8 we created a USMT 4 package to migrate the users data using hardlinking and then we imported the captured image into ConfigMgr and created a Deploy Windows 7 X64 task sequence. We created a Deploy Windows 7 X64 Collection and set some User Device Affinity collection variables. In Part 9 we created an Application, and created a deployment type for that application to only install if the Primary User was True for that device (User Device Affinity), we then copied our Task Sequence (duplicated it), deployed the new Task Sequence, added a computer to the new collection and then PXE booted the computer to the Deployment Menu. In Part 10 we monitored the Deployment process in a lot of detail to how UDA sent state messages and we verified that our application installed on the users Primary Device, in addition we modified our collection variables, and added a prestart command to our boot image to prompt for the SMSTSUdaUsers. In Part 11 we setup the Reporting Services Point Role and verified that reporting was working. In Part 12 we demonstrated a new feature in ConfigMgr which allows us to Patch operating system WIM images using Offline Servicing. This means that you can apply Windows Updates by using Component-Based Servicing (CBS) to update the your previously captured WIM images. Now we will look at how Role Based Administration is used within ConfigMgr and we will create a new custom role to allow a user (or users within a Security Group) to view Software Update Reports. This is useful because you will probably want one team to take care of configuring and deploying software updates, and to grant another (Management etc) the capability of reviewing Compliance Reports. Note: From this point on, all parts in this series will be created using Configuration Manager 2012 Release Candidate 2 unless otherwise specified. For more information about Role Based Administration and for best practise advice please review the following:- Technet:- Security: Role-Based Administration Section of Whats new in Configuration Manager 2012 here Planning for Security in Configuration Manager 2012 - http://technet.micro...y/gg712284.aspx Introducing Role-Based Administration in System Center 2012 Configuration Manager - http://blogs.technet...on-manager.aspx Step 1. Understanding Role Based Administration In Configuration Manager 2007, administrative access to site resources is controlled by using class and instance security settings that are verified by the SMS Provider computer to allow access to site information and configuration settings. System Center 2012 Configuration Manager introduces role-based administration to centrally define and manage hierarchy-wide security access settings for all sites and site settings. Instead of using individual class rights, role-based administration uses security roles to group typical administrative tasks that are assigned to multiple administrative users. Security scopes replace individual instance rights per object to group the permissions that are applied to site objects. The combination of security roles, security scopes, and collections allow you to segregate the administrative assignments that meet your organization requirements and this combination defines what an administrative user can view and manage in the Configuration Manager hierarchy. Role-based administration provides the following benefits: Sites are no longer administrative boundaries. They were with Configuration Manager 2007. You create administrative users for the hierarchy and assign security to them one time only. You create content for the hierarchy and assign security to that content one time only. All security assignments are replicated and available throughout the hierarchy. There are built-in security roles to assign the typical administration tasks and you can create your own custom security roles. Administrative users see only the objects that they have permissions to manage. You can audit administrative security actions What roles are included ? The following 14 built in security roles are included:- Operations Administrator Full Administrator Infrastructure Administrator Security Administrator Software Update Manager Read-Only Analyst Remote Tools Operator Operating System Deployment Manager Application Deployment Manager Application Author Application Administrator Asset Manager Endpoint Protection Manager Compliance Settings Manager Step 2. Implementing a custom security role. Perform the following on your Configuration Manager 2012 server as SMSadmin. In the ConfigMgr console, click on Administration and expand Security, click on Security Roles. The 14 built-in roles appear. We want to create a custom security role to allow users assigned to that role to read Software Update Reports. As there is no option to create a blank new role, we must use the Copy function to create our new security role. Select the built-in Software Updates Manager role, right click and choose Copy. When the Copy Security Role wizard appears, give the new role a name based on the function, you can name the new role as follows:- SUM Reports Reader it's also a good idea to fill in a Description of the role as per the screenshot below, notice all the predefined permissions assigned to the Software Updates Manager role appear selected in the Permissions pane. We will edit these to only leave those permissions that are required to run reports. using the Customize the permissions for this copy of the security role, expand any permission not required and change it from YES to NO (you can double click on each one to change). For example, expand the Alerts permissions and set them all to NO as none of these permissions is required to read reports. Configure the Permissions so the only the following are set to Yes Site: Read Software Updates: Read, Run Report Click OK when done, the custom SUM Reports Reader role now appears in your console. Step 3. Create a Global Security Group in Active Directory Perform the following on your Active Directory Domain Controller server as Domain Administrator. Now that we have created our custom security role, we want to assign users to that role. In Active Directory Users and Computers create a new Global Security Group called Software Updates Management Report Readers as per the screenshot below. To create a new global security group, right click on Users, select New, Group. Add some users to that group by selecting those users and right-clicking, choose Add to a Group when the Select Groups wizard appears, type in the name of our security group and click on Check Names, click ok when done. you've now added some users to the Active Directory security group called Software Updates Management Report Readers. Step 4. Assign the Active Directory Security Group to our custom role Perform the following on your Configuration Manager 2012 server as SMSadmin. In the Administration pane, expand security and select Administrative Users. In the ribbon click on Add User or Group when the Add User or Group wizard appears select browse and search for our previously created Active Directory Security Group, type in Software Updates Management Report Readers and click ok next we need to assign this group with our custom role, so select Add to add security roles, scroll through the list of roles and select our custom role: SUM Reports Reader as per the screenshot below Click OK when done (leave the Assigned security scopes and collections as they are) Our active directory security group is now assigned the custom SUM Reports Reader security role. Step 5. Verify the custom role has the permissions we need Perform the following on your Configuration Manager 2012 server as a member of the Software Updates Management Report Readers active directory security group. We will now test our new custom role by starting the Configuration Manager console as a user which is a member of the previously created active directory security group. To do this right click on the Configuration Manager console icon in the system tray and hold down the shift key, then right click again (while holding down shift) on the new configuration manager console icon so that we can get a context based menu option called Run as Different User. when the security credentials window appears, type in the credentials of a domain user that you have previously added to the Software Updates Management Report Readers active directory security group, click ok when done. After a while, the Configuration Manager console will appear as it would if started by that user and you can immediatly see that it looks different, only the bits that are relevant to this user running Software Update reports are displayed in the console. When you add (or remove) permissions from the role, this view will change however you should close and re-open the console to see the new view with the credentials of your desired user. We have already defined our permissions so lets select Monitoring and expand Reporting and then select Reports. Notice how only 48 software update related reports appear (in comparison to the 445 or so reports that a member of the Full Administrator security role would be able to view). and below is what a Full Administrator would see in the same Reports pane The difference in the number and type of reports available and what you can do/see in the Configuration Manager console is governed by Role Based Administration, cool huh ?


-
Introducing: The BitLocker Frontend HTA
anyweb replied to anyweb's question in Frontends, HTA's and Web Services
if you exit diskpart can you dir c:\ ? -
they must press F12 twice !, the first time gets the network ip address, contacts WDS, downloads some files, the second is to start network boot proper so that you can start your task sequences, so that user must press F12 when stated on screen, is your issue similar ?
-
you MUST press F12 for network boot when you see that message, have you tried that.... ?
-
Installation Part 1: how can I install SMS 2003 SP2? Part 2: how can I configure SMS 2003 ? Part 3: SMS 2003 final configuration Configuration how can I deploy an application using SMS ? how can I upgrade SMS 2003 to SCCM 2007
-
the collation must be as specified, have you tried reinstalling sql from scratch ? if it's a virtual machine should be easy to revert...
-
i mean, what does the actual application that you are trying to install, that MSI log file say, not the appenforce.log...
-
before you see this error what do you see on screen ?
-
here is a list of some of the System Center Operations Manager 2007 Guides I've put together. Installation Part 1. Create AD accounts Part 2. Install IIS and required role services Part 3. Install SQL Server 2005 sp3 Part 4. Install Operations Manager 2007 configuration Now that you have Setup Operations Manager 2007, you will need to configure it. Part 1. Configure Computers and Devices to Manage Part 2. Import Management Packs Part 3. Configure Reporting
-
what does the application installation LOG file tell you
-
Task sequence fails by Setup windows and configmgr
anyweb replied to StefanWe's topic in Configuration Manager 2012
c:\windows\debug\netsetup.log will cover domain join failures, look at that log file -
i'll be covering migration soon in a new post, watch this space
-
Introducing: The BitLocker Frontend HTA
anyweb replied to anyweb's question in Frontends, HTA's and Web Services
hmm that shouldnt happen, can you take a screenshot/photo of what you are seeing please, and include diskpart info for me also (bring up a command prompt and run diskpart, select disk 0, list par -
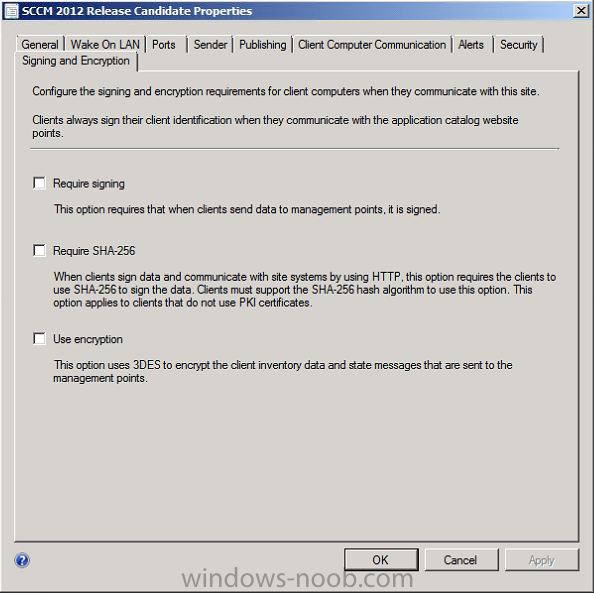
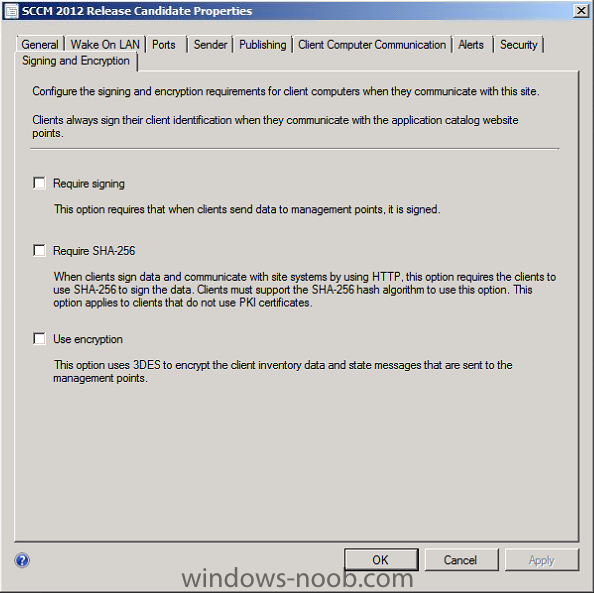
It is currently in the Site Properties of your site, under the Signing and Encryption tab, It was re-worded and now says: Require SHA-256.
-
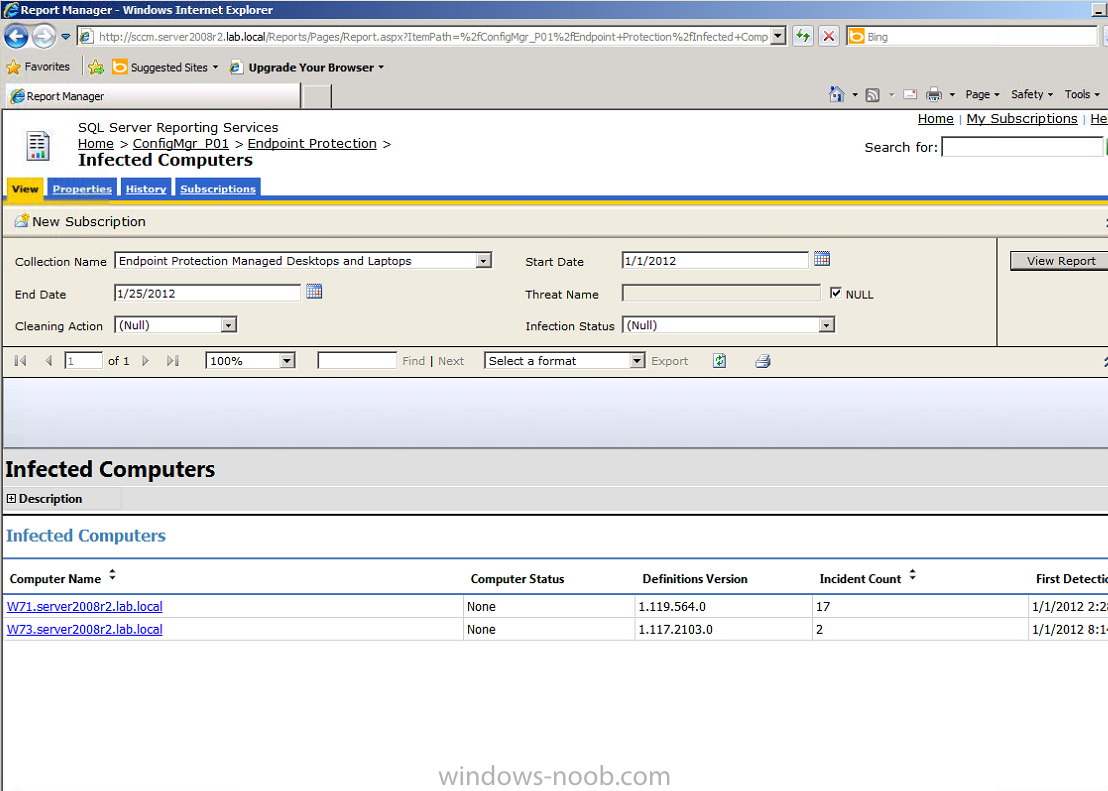
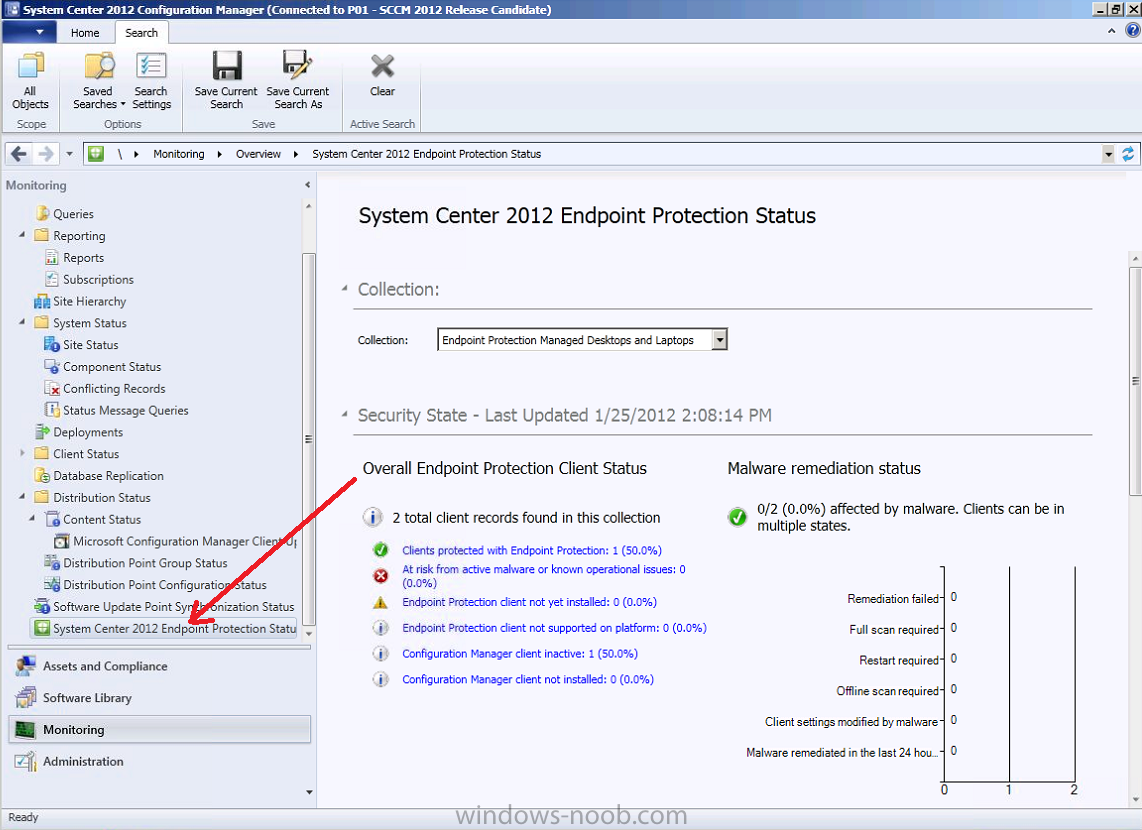
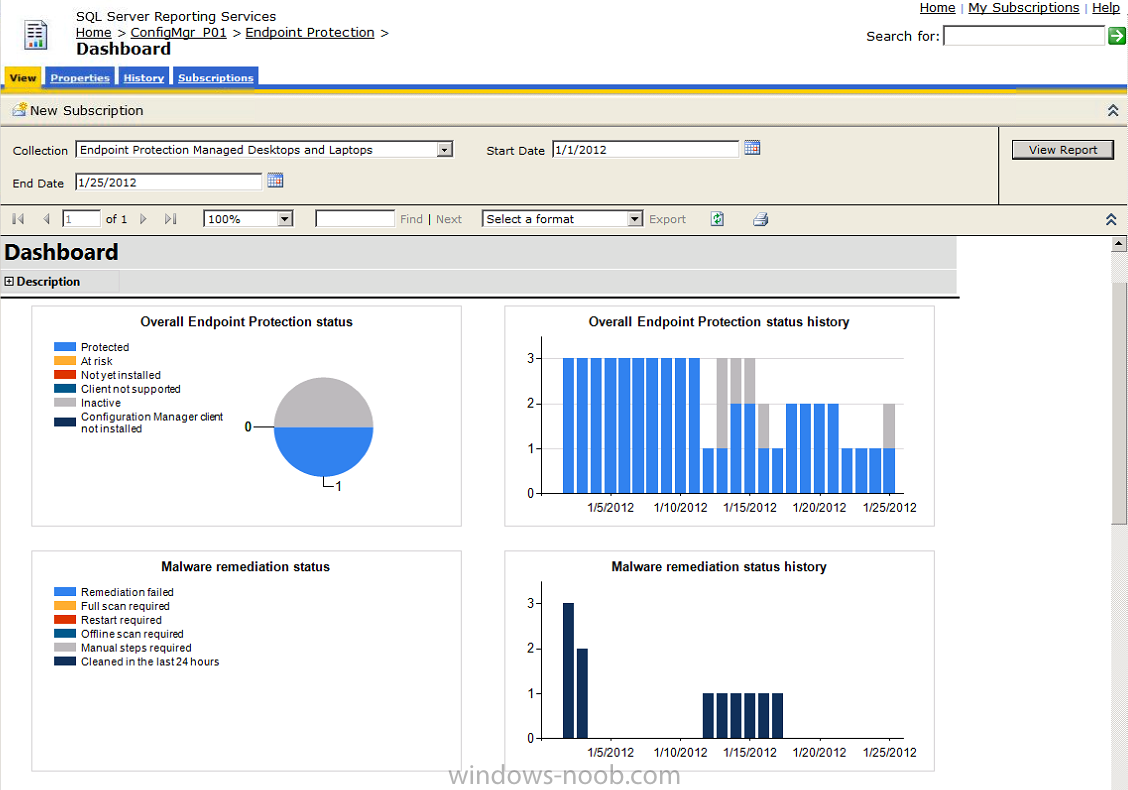
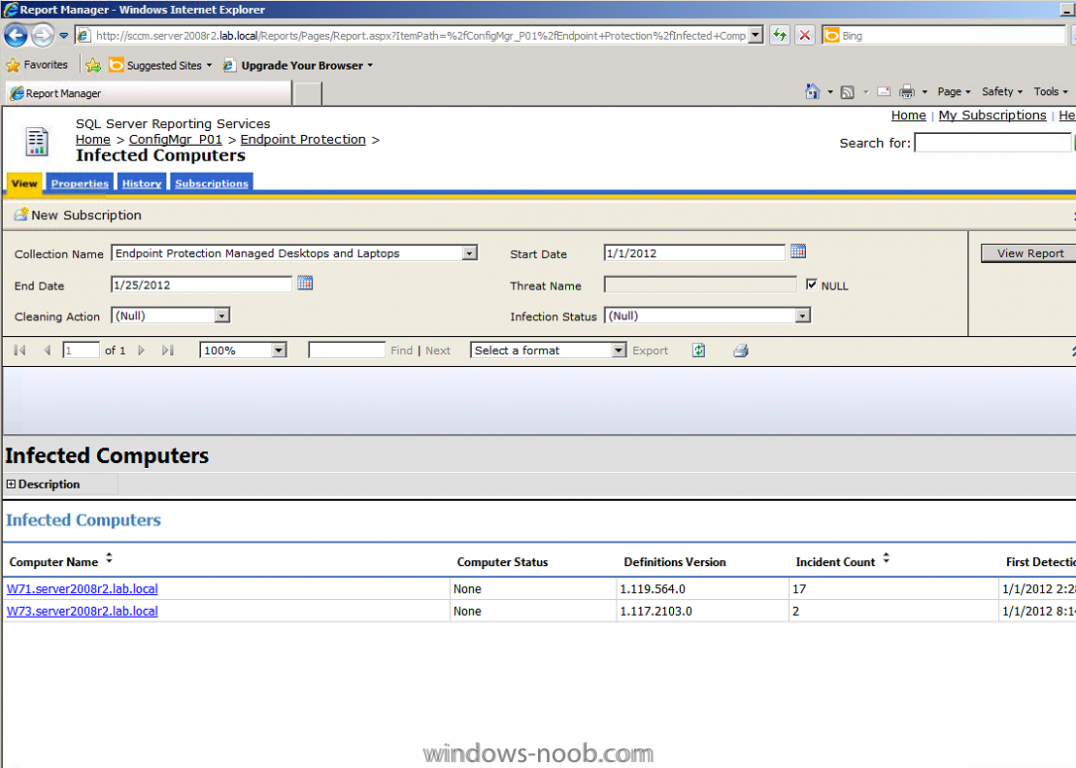
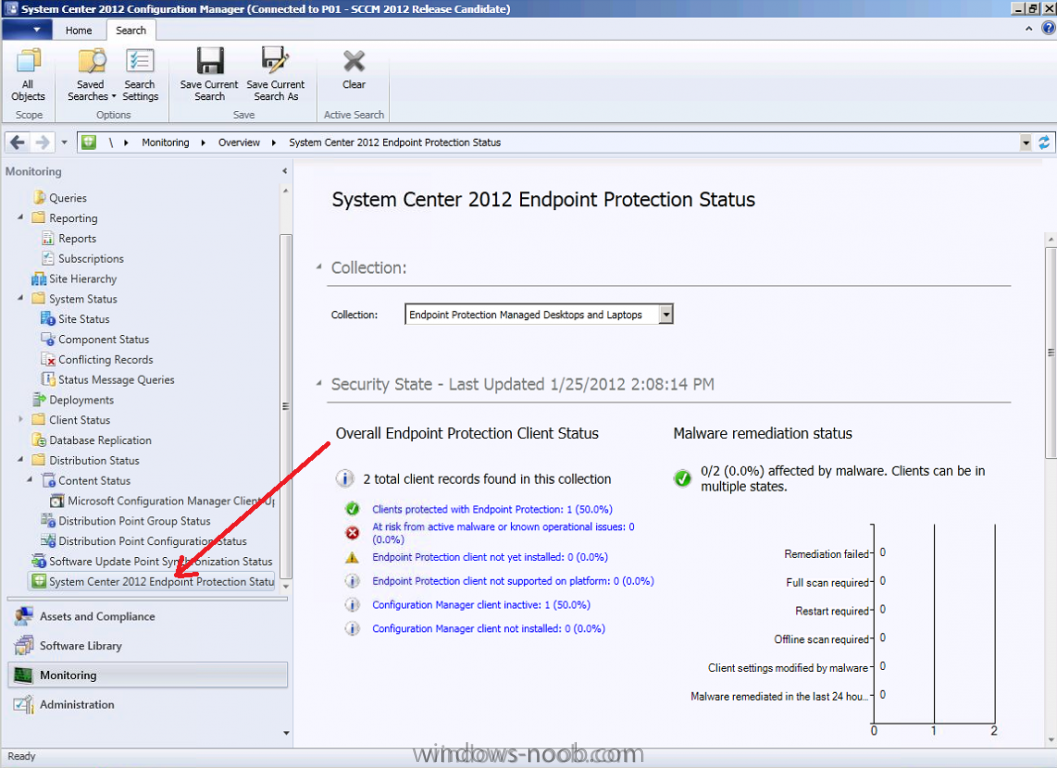
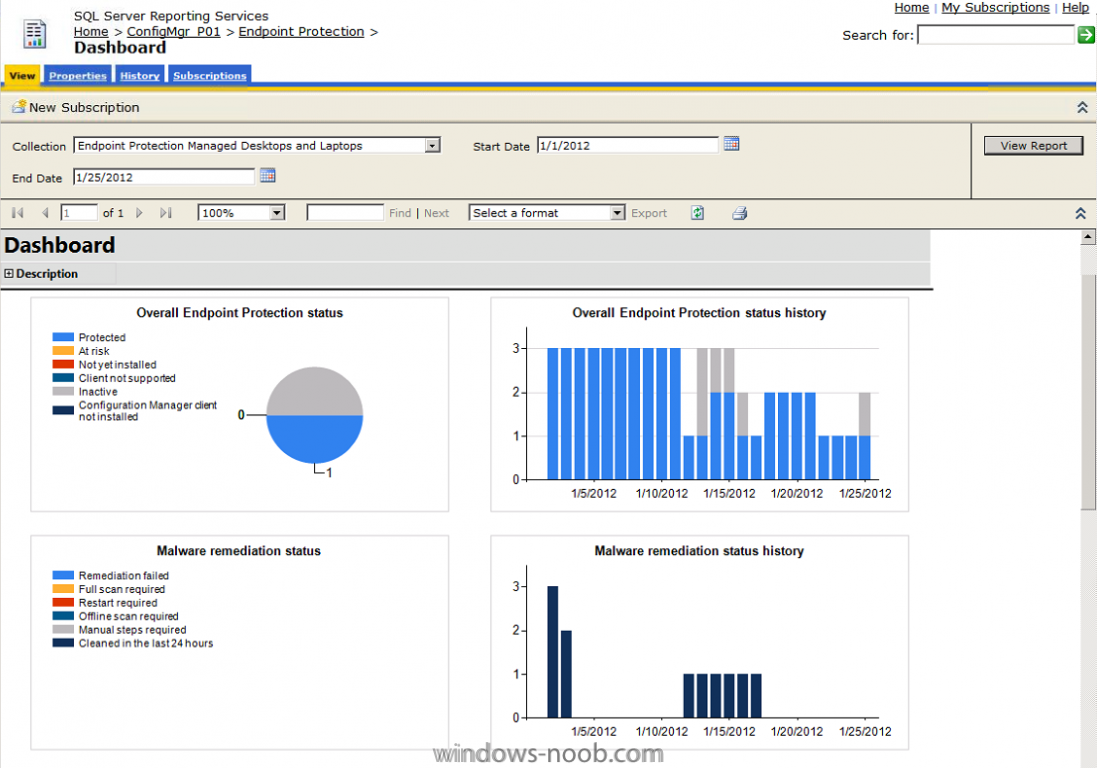
Up until recently, Endpoint Protection came with 4 built-in reports in Configuration Manager 2012. AntiMalware Activity Report Computer Malware Details Top Users By Threats User Threat List As of RC2 there are now six built-in reports AntiMalware Activity Report Computer Malware Details Top Users By Threats User Threat List Infected Computers Dashboard so what are the new reports about ? The fist new Endpoint Protection report shows a nice list of Infected Computers in a timeframe that you can select, you can verify what type of remediation was done via drop down menu and even search by Threat Name (see below). Next we have the Dashboard Report, this report shows lots of nice graphs to give you a graphical view of overall Endpoint Protection status in the collection you selected, malware remediation status, Operation Status of Endpoint Protection clients, Definiton status on Computers (see below) In other words, this report shows summaries of what you can see in the In-console monitoring Endpoint Protection Dashboard in the Monitoring node of the ConfigMgr Console. all in all, very cool stuff, if you havn't yet started experimenting with Endpoint Protection in Configuration Manager 2012 then get started, it's a Blast !
-
how did you setup SQL and what version of sql did you use
-
BUILD and Capture Windows 7 Enterprise for VDI
anyweb replied to jamitupya's topic in Configuration Manager 2012
you must install the client otherwise the task sequence will fail. -
Introducing: The BitLocker Frontend HTA
anyweb replied to anyweb's question in Frontends, HTA's and Web Services
that's a known issue, just diskpart your hard disc, make sure its got a partition and is formatted and then try again, it'll display correctly -
BUILD and Capture Windows 7 Enterprise for VDI
anyweb replied to jamitupya's topic in Configuration Manager 2012
here's your error Task sequence cannot continue after reboot because TS Manager is not configured to auto-start or GINA is not installedwhich probably happened due to the configmgr client failing to install, so examine your ccmsetup.log file to see what it tells you -
Much trouble with OSD installation and first steps
anyweb replied to StefanWe's topic in Configuration Manager 2012
is it a vmware environment ? perhaps you have a vmware dhcp server causing issues... -
well you can't have a tree view or folders, unfortunately
-
verify DNS, on any of the clients do nslookup. can you ping the fqdn of the Configmgr server ? and vice versa to the clients ? tell me exactly what steps you are taking to deploy the client ?
-
Summary: The coming Windows 8 beta is looking more and more like it will be called the “consumer preview.” Why the change in nomenclature? Is Microsoft going to position the coming Windows 8 beta as a “consumer preview”? And if so, why? Microsoft officials have repeated recently that the Windows 8 beta release is on track for late February 2012. But one public relations official with the Windows team provided a slightly different message — and one that escaped notice by most of those who read her quote — during the Consumer Electronics Show. As reported by Pocket Lint, Windows Director of Consumer PR, Janelle Poole, stayed on message regarding Microsoft’s continued reluctance to talk about its release-to-manufacturing/ship targets for Windows 8. But, as Windows SuperSite’s Paul Thurrott noted last week, part of Poole’s message deviated from the usual script. Poole called the coming Windows 8 beta “the consumer preview.” Here’s her quote: “We haven’t talked about the release date and we generally don’t. We are talking milestone to milestone, so for us right now we’re talking about the next milestone being the consumer preview happening in late February.” If you know anything about the Windows org, you know words matter. This wasn’t a random throw-away. My first question was whether it’s just the internal Windows consumer PR team calling the beta “the consumer preview” or if the Microsoft brass plan to do the same. I’m hearing that the Windows organization is highly likely to settle on “consumer preview” as the name for the late-February beta. The bigger question — which Thurrott and I discussed during the most recent episode of Windows Weekly — is why Microsoft may label this the consumer preview. Thurrott’s theory was that maybe the developer preview (the September Build version) will be followed by a consumer preview (the beta) and finally the enterprise preview (the release candidate). My theory is more cynical, but not entirely unwarranted. I believe if Microsoft changes the nomenclature, the company is doing so to signify a change that’s been coming for a while now. What used to constitute a “beta” doesn’t really exist in the new Windows world. I said the same during the Windows 7 test period: That the current Windows organization doesn’t show code publicly at all until it’s pretty much set in stone and going to be tweaked very minimally. This makes Windows more predictable, but it also implies that the product is far less likely to incorporate suggested fixes from those outside Microsoft. During the Windows 7 test period, there were still a select group of technical beta testers on whom Microsoft seemingly leaned for real feedback and guidance regarding the product. That team, known internally as the “Test Pilots,” was disbanded after Windows 7 was released. As far as I know, there’s no equivalent to this group this time around. And Senior Program Manager for technical beta testing for Windows, Paul Donnelly, recently left Microsoft to go to Amazon with no replacement named (again, as far as I know). There could be other reasons Microsoft may prefer the “consumer preview” name to “beta.” By claiming a product is far enough along to be used by plain old consumers — and not just techie beta testers — Microsoft officials could be hoping to convince those who think a possible Q3 Windows 8 launch will be too late for Microsoft to shoe-horn its way into the tablet space that Windows 8 is right around the corner. (”Hey, it’s basically done — it’s in consumer preview now!”) Such a name also could help Microsoft’s PC partners who need a way to make new tablets and PCs that they’re bringing to market from now until the time that Windows 8 is shipping seem more up-to-date and palatable. (”This runs the Windows 8 Consumer Preview — so you know it’ll be able to run the final Windows 8 with no problem.”) Microsoft officials aren’t saying anything beyond the fact that the next Windows 8 release is due out in late February and that there is no separate “consumer preview” in the works — meaning, to me, the one-and-only Windows 8 beta is highly likely to be called the “Consumer Preview” when it is released. What’s your take as to why Microsoft is leaning toward calling the beta a “consumer preview” — and what effect (if any) this will have on Redmond, its developers, partners and customers? Thoughts? via > http://www.zdnet.com/blog/microsoft/windows-8-why-the-coming-beta-is-likely-to-be-labeled-the-consumer-preview/11716
-
Much trouble with OSD installation and first steps
anyweb replied to StefanWe's topic in Configuration Manager 2012
is the wds service hanging ? disable the PXE password on it (remove it) on the PXE tab of your distribution point, try restarting/starting the wds service -
Much trouble with OSD installation and first steps
anyweb replied to StefanWe's topic in Configuration Manager 2012
did you distribute BOTH architecture boot images to your dps ?